Auditant
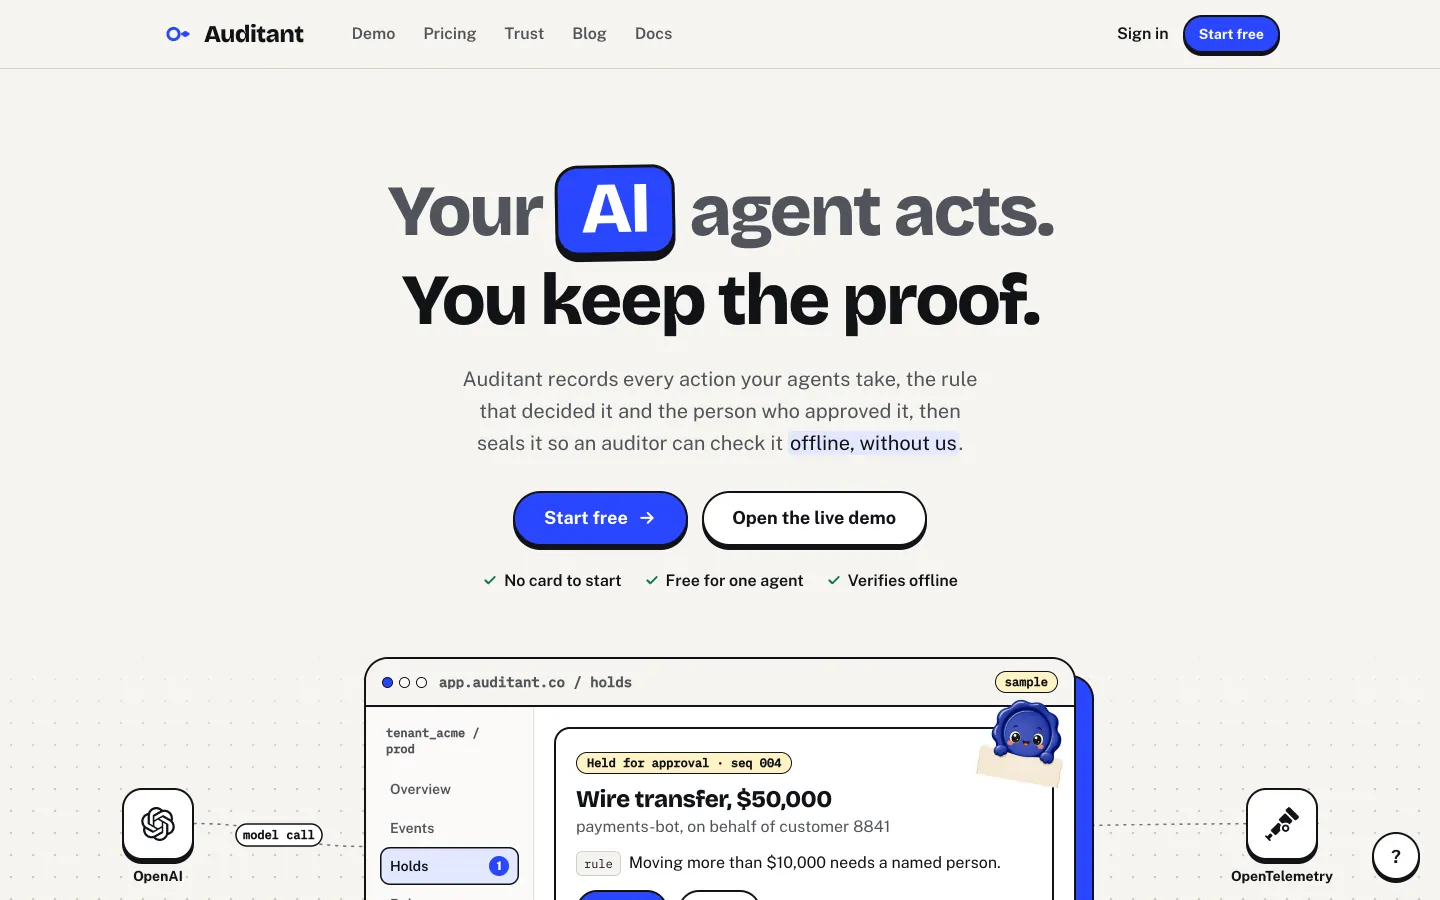
The compliance system-of-record for AI agents
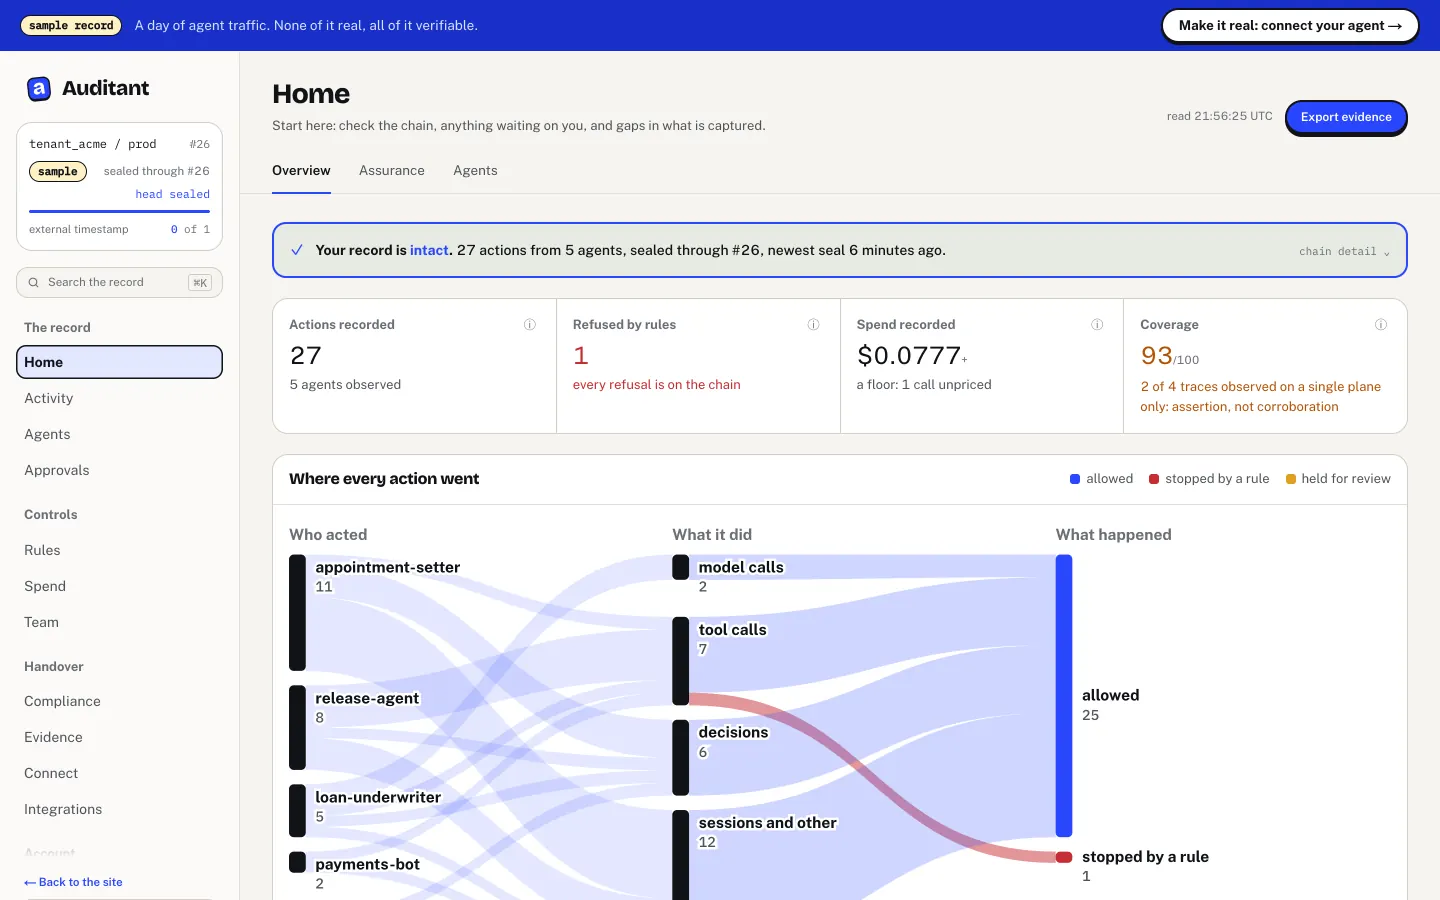
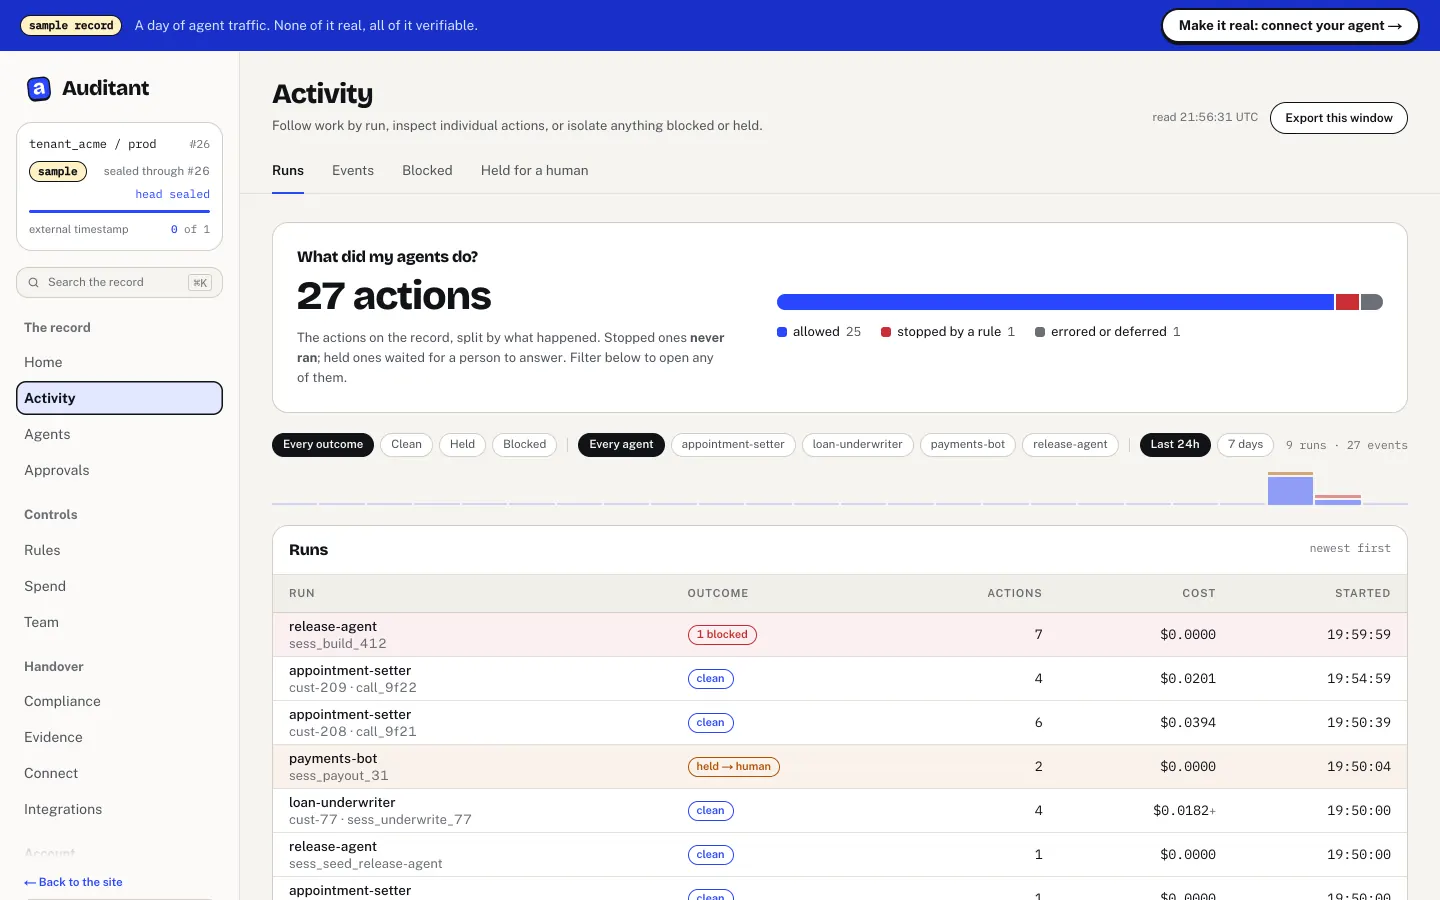
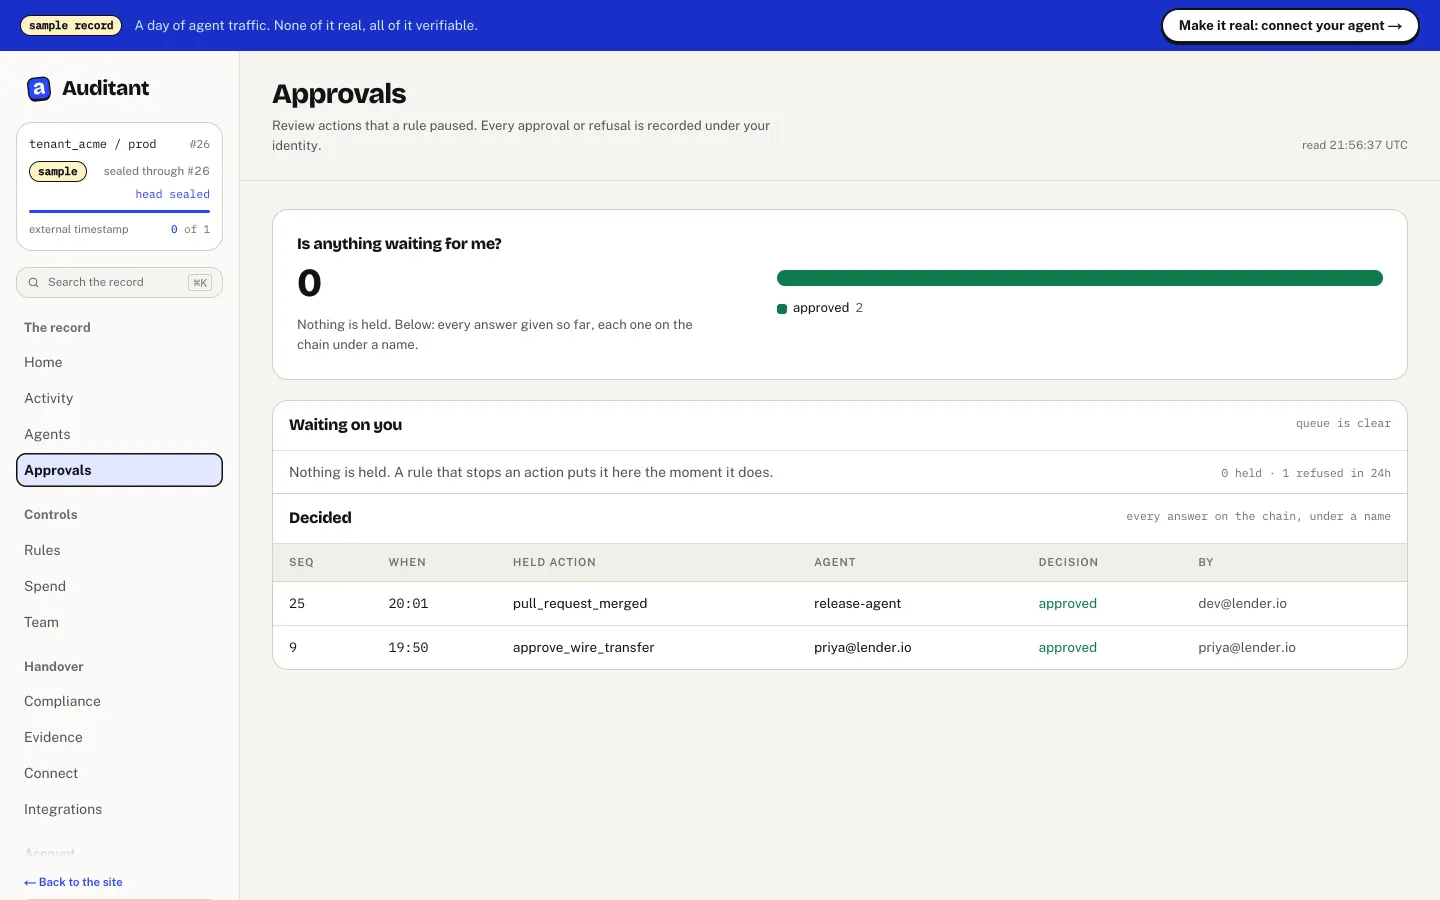
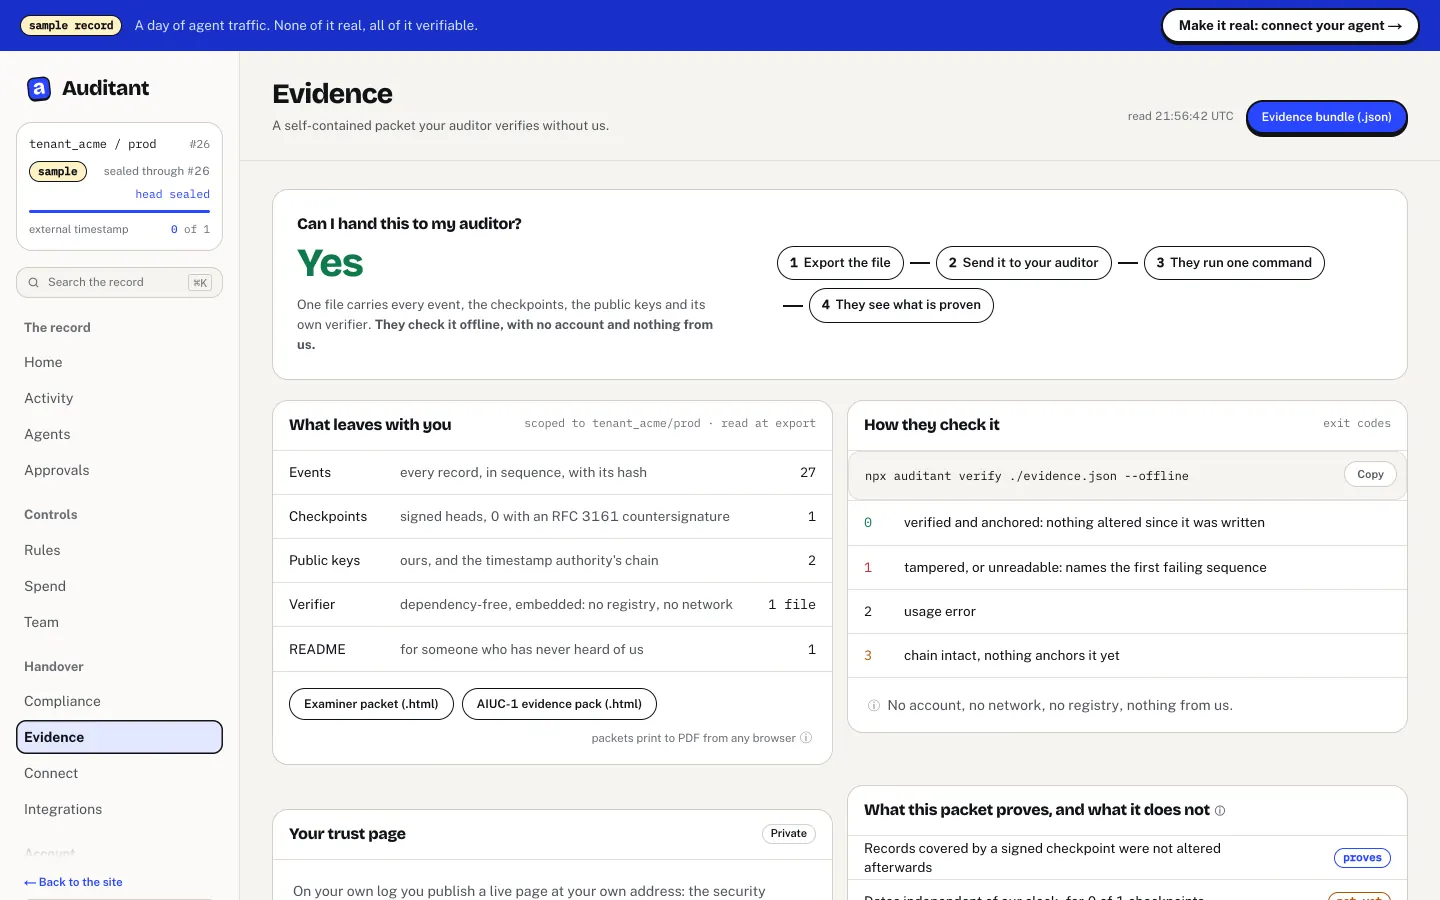
Every agent action lands in a tamper-evident, hash-chained log. Policy checks run before execution. Evidence exports verify offline, with no account and no vendor.
The problem
AI agents approve loans, move money, and ship code, but no reliable record exists of what they did or why. Logs are scattered across the app, the model provider, and the framework: none built for an auditor, all mutable, and most deleted long before anyone asks. Provider audit trails purge in days while regulations demand years.
How I built it
Built a system-of-record that streams every agent action into a tamper-evident, hash-chained log, evaluates each action against policy before it executes, and exports evidence bundles a regulator can verify offline, without an account and without the vendor. Events from all four planes (application, model provider, framework, infrastructure) normalize into one auditable schema.
The hard parts
- Tamper evidence that holds up: hash-chained records with verification tooling that catches a single flipped byte anywhere in the chain
- Policy checks in the hot path: evaluating every action before execution without adding meaningful latency to the agent loop
- Offline verification with zero vendor dependency: an auditor who has never heard of the product can validate an evidence bundle
- Normalizing four different event planes (app, provider, framework, infra) into one schema an auditor can actually read